Virtual event security risks start at the hosting layer
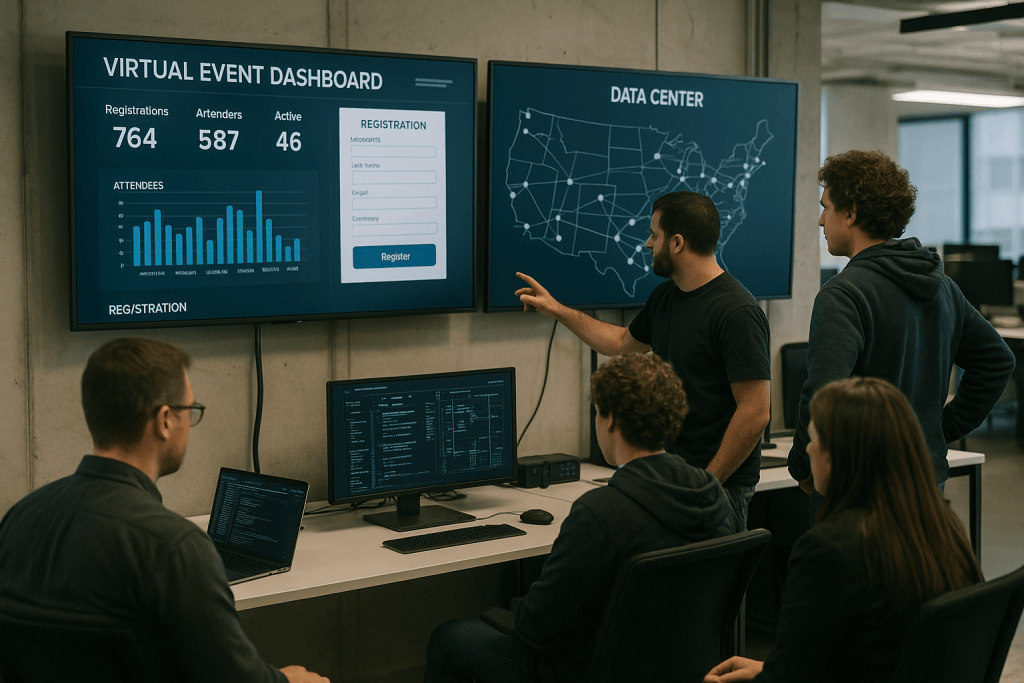
As virtual and hybrid events have become a permanent fixture of the business landscape, their underlying security practices are facing deeper scrutiny. Behind seemingly simple registration forms lies a complex web of personal and sensitive data collection that many organisers may be underestimating, particularly in relation to hosting choices and regulatory obligations.
From names and job titles to accessibility needs and dietary preferences, today’s event platforms routinely gather information that can expose special category data under privacy regulations. For event planners and technology providers, this raises pressing questions about where that data lives, who can access it, and how robustly it is protected throughout the event lifecycle.
Background: more data, more risk in digital events
Before the rapid shift to virtual and hybrid formats, in-person conferences already handled a substantial amount of attendee information. However, the move to digital delivery has amplified both the volume and sensitivity of data processed. Every interaction – registration, session attendance, live chat, Q&A participation, polling, networking, and content downloads – can be logged, stored and analysed.
Hybrid events add another layer of complexity, combining physical check-in systems with online attendee journeys spread across web platforms, mobile apps, streaming services and CRM or marketing tools. Each system introduces additional data flows and potential exposure points for information about individuals’ identities, behaviours, and in some cases health or belief-related details.
Regulations such as the EU’s General Data Protection Regulation (GDPR) and similar frameworks elsewhere place strict conditions on how such information is collected, stored and transferred. Yet in practice, event teams are often focused on experience design, engagement metrics and commercial outcomes, with security and privacy considerations arriving later in the planning cycle – if at all.
Key developments: sensitive data hiding in plain sight
Even a modest professional conference will typically request a mix of basic and sensitive information during registration. Core fields like name, email address, employer and job title are now routinely supplemented with dietary preferences, accessibility needs, travel details, and customised questions set by the organiser or sponsor. For paid events, payment data may flow through connected systems as well.
Some of these fields can reveal attributes that regulators treat as particularly sensitive. Dietary requirements may imply religious observance or health status; accessibility needs can point to physical or mental health conditions. When combined with professional profiles and company information, this can create rich datasets with heightened privacy implications.
The security question begins not with encryption standards alone, but with where and how this data is hosted. Many virtual event platforms rely on third-party infrastructure providers, content delivery networks, or embedded services for payment and analytics. Others deploy white-labelled solutions or integrate multiple tools to deliver registration, streaming, networking and follow-up campaigns.
Every hosting decision – from the primary data centre location to the configuration of content delivery and backups – can affect regulatory compliance, data residency, and the risk of unauthorised access. Cross-border data transfers and the involvement of subcontracted service providers complicate the picture further, especially for events with international audiences.
Industry impact: compliance, trust and commercial risk
For event organisers and platform vendors, the implications are significant. A single misconfigured database, unsecured API, or unclear hosting arrangement can expose attendee information, trigger regulatory investigations and damage client relationships. Beyond fines or legal action, reputational harm can be severe in a sector built on professional trust and brand partnerships.
Corporate clients are increasingly enquiring about how event data is handled, where it is stored, and which parties have access. Procurement teams and IT security departments are more involved in platform selection, requesting documentation on hosting locations, security certifications and data processing agreements. What was once a back-of-house technical detail is quickly becoming a competitive differentiator.
Platform providers, meanwhile, must navigate a complex environment of cloud infrastructure choices, regional data protection rules and client-specific requirements. Decisions on whether to host in specific regions, use multi-tenant architectures, or rely on global content networks now have direct implications for sales to regulated sectors such as finance, healthcare, and government.
Hybrid event formats bring added pressure. Onsite registration systems, badge printing, lead retrieval tools and venue Wi-Fi networks all interact with the same datasets managed by virtual platforms. Coordinating secure data flows across these touchpoints requires clear governance and technical alignment between organisers, technology providers and venues.
Why this matters for event professionals and technology providers
For event professionals, security and hosting considerations are no longer optional technical line items. They influence contractual risk, audience confidence and the ability to serve clients with strict compliance obligations. Several practical implications emerge:
- Platform selection criteria are evolving. Beyond engagement features and analytics, buyers are asking where attendee data is hosted, what encryption is used at rest and in transit, and how access controls are managed internally and with subcontractors.
- Registration design requires greater care. Fields that may reveal health or religious information need clear justification, minimisation and explicit communication in privacy notices. Organisers must ensure their chosen platform can handle such data in line with applicable regulations.
- Contracting and data processing agreements are critical. Roles and responsibilities between organisers, platforms, and infrastructure providers need to be clearly documented, including data residency commitments and breach response procedures.
- Hybrid workflows must be mapped end-to-end. From initial registration through onsite check-in to post-event marketing, each system that touches attendee data should be identified, with hosting locations and security measures understood.
- Training and awareness are part of the solution. Event teams, not just IT staff, need a working understanding of how their choices on forms, integrations and tools affect security and privacy outcomes.
Technology providers in the event space are similarly affected. Demonstrable security posture, transparent hosting arrangements, and the ability to adapt to client-specific data residency needs are increasingly central to platform roadmaps and go-to-market strategies. Differentiation may come from clearer documentation, independent certifications, or the flexibility to host data in multiple jurisdictions.
Conclusion
As digital, hybrid and on-demand formats become standard for conferences and exhibitions, the security perimeter of an event has expanded far beyond the walls of a venue. It now begins with the design of an online form and extends through hosting infrastructure, third-party integrations and post-event data use.
Virtual event security is therefore not solely a matter of adding more safeguards around content streams or logins. It is fundamentally shaped by where attendee information is stored, how it flows between systems and which partners are involved in processing it. Addressing these questions early in planning, and embedding them into vendor selection and contractual frameworks, will be central to building resilient, compliant and trusted event experiences in the years ahead.