Biometric-Free Authentication: Privacy-First Identity Verification Systems
7 months ago Timothy Myres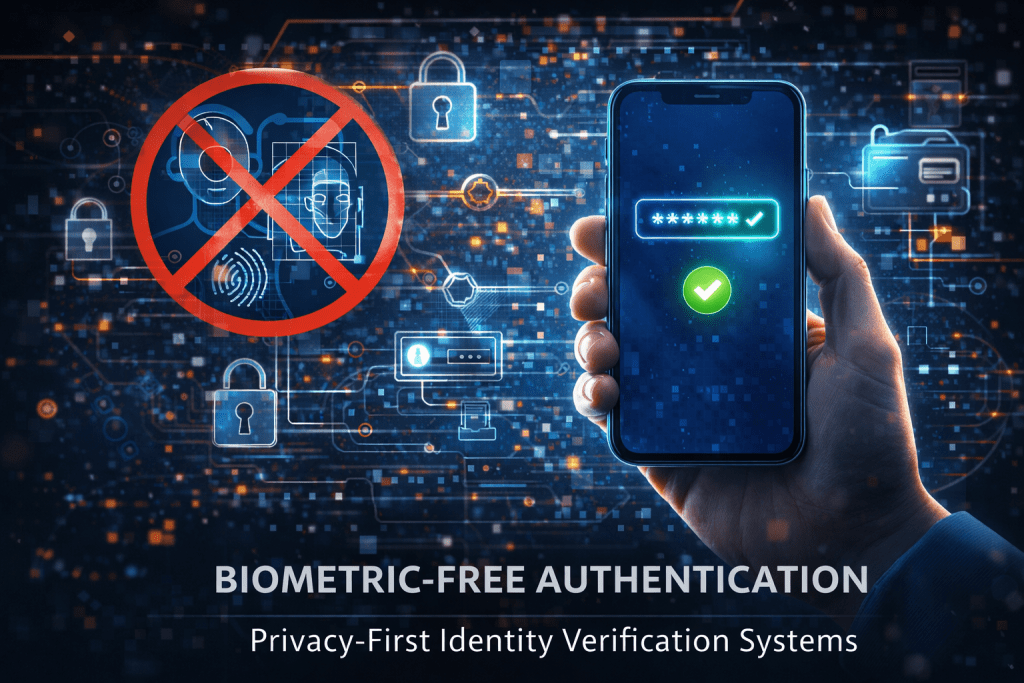
Introduction: Rethinking Identity in Data-Sensitive Event Environments
Table of Contents
ToggleAs event ecosystems become increasingly digital, identity verification has become a foundational layer for access control, personalization, payments, and security. Traditional approaches—ranging from QR codes to RFID badges—are now being augmented or replaced by biometric systems such as facial recognition and fingerprint scanning. While biometrics offer convenience and speed, they introduce significant privacy, regulatory, and ethical concerns.
In response, a new class of identity systems is emerging: biometric-free, privacy-first authentication frameworks. These systems aim to deliver secure, seamless identity verification without relying on immutable personal identifiers. For event technology platforms, this shift is not merely about compliance—it is about building trust, reducing risk, and enabling scalable identity management across increasingly complex event environments.
Why Move Away from Biometrics?
Biometric systems present several structural challenges:
-
Irreversibility: Unlike passwords, biometric data cannot be changed if compromised
-
Centralization risks: Storing biometric templates creates high-value attack targets
-
Regulatory constraints: Increasing scrutiny under global data protection laws
-
User resistance: Growing awareness of surveillance and privacy implications
In event contexts—where attendees may be transient, international, and privacy-conscious—these challenges are amplified. Biometric-free systems offer an alternative that balances security with user control.
Core Principles of Privacy-First Authentication
1. Data Minimization
Only essential identity data is collected and processed. Systems avoid storing sensitive personal attributes unless absolutely necessary.
2. Decentralization
Identity credentials are stored and controlled by the user rather than centralized databases. This reduces breach risks and enhances privacy.
3. Verifiability Without Exposure
Authentication systems should confirm identity or eligibility without revealing underlying personal data. This is often achieved through cryptographic proofs.
4. Interoperability
Identity systems must function across multiple platforms, vendors, and event environments without requiring redundant registrations.
Key Technologies Enabling Biometric-Free Authentication
1. Decentralized Identity (DID)
Decentralized Identity frameworks allow users to own and manage their digital identities באמצעות cryptographic keys.
-
Identity data is stored in digital wallets
-
Verification is performed באמצעות decentralized identifiers
-
No central authority controls the identity
DIDs enable attendees to reuse credentials across events without exposing sensitive information.
2. Verifiable Credentials (VCs)
Verifiable credentials are digitally signed attestations issued by trusted entities:
-
Event organizers
-
Ticketing platforms
-
Accreditation bodies
Examples include:
-
Event tickets
-
VIP access credentials
-
Professional certifications
These credentials can be presented and verified without contacting the issuer in real time.
3. Zero-Knowledge Proofs (ZKPs)
ZKPs allow users to prove a statement without revealing the underlying data.
For example:
-
Proving age eligibility without revealing date of birth
-
Confirming ticket ownership without exposing identity
This is particularly valuable for privacy-sensitive event scenarios.
4. Token-Based Authentication
Instead of persistent identifiers, systems use:
-
Time-bound tokens
-
One-time access credentials
-
Cryptographically signed session tokens
These reduce the risk of long-term data exposure.
5. Device-Bound Credentials
Authentication can be tied to user devices:
-
Secure enclaves in smartphones
-
Hardware-backed key storage
-
Passkeys and passwordless authentication
This enables strong security without biometrics.
System Architecture for Privacy-First Identity
Identity Issuance Layer
-
Credential generation (tickets, badges)
-
Digital signing using cryptographic keys
-
Distribution to user wallets
Wallet and Storage Layer
-
Mobile or web-based identity wallets
-
Secure key management
-
User-controlled credential storage
Verification Layer
-
Scanners or gateways validating credentials
-
Cryptographic verification (signature checks)
-
Offline verification capabilities
Integration Layer
-
APIs connecting identity systems with event platforms
-
Access control systems (entry gates, session check-ins)
-
CRM and analytics systems (with privacy-preserving data flows)
Audit and Compliance Layer
-
Logging of verification events (without exposing personal data)
-
Compliance with data protection regulations
-
Transparency and user consent mechanisms
Real-World Event Applications
Secure Event Entry
Attendees can:
-
Present digital credentials via mobile wallets
-
Verify access without revealing personal identity
-
Enter venues through fast, contactless checkpoints
Role-Based Access Control
Different attendee types (VIPs, speakers, staff) can:
-
Hold credentials defining access rights
-
Gain entry to restricted areas without manual checks
Cross-Event Identity Portability
Frequent attendees can:
-
Reuse credentials across multiple events
-
Avoid repeated registration processes
-
Maintain consistent identity without centralized storage
Sponsor and Networking Interactions
Instead of sharing personal data:
-
Attendees can selectively disclose information
-
Exchange verifiable credentials (e.g., professional roles)
-
Maintain privacy while enabling meaningful connections
Operational and Business Impact
Enhanced Privacy and Trust
Privacy-first systems:
-
Reduce data exposure risks
-
Build attendee confidence
-
Align with evolving regulatory expectations
Reduced Liability
By avoiding storage of sensitive data:
-
आयोजकों reduce breach risks
-
Compliance costs are minimized
-
Legal exposure is limited
Improved User Experience
Passwordless, token-based systems offer:
-
Faster authentication
-
أقل friction during event entry
-
Seamless cross-platform experiences
Scalability
Decentralized systems scale more effectively:
-
No central bottlenecks
-
Distributed verification processes
-
Resilience against system failures
Challenges and Considerations
User Adoption and Education
New identity paradigms require:
-
Clear onboarding processes
-
Intuitive wallet interfaces
-
User trust in unfamiliar technologies
Infrastructure Readiness
Event venues and platforms must support:
-
Credential scanning and verification
-
Integration with identity APIs
-
Offline verification capabilities
Interoperability Standards
The ecosystem is still evolving:
-
Multiple DID and VC standards
-
Limited cross-platform compatibility
-
Need for industry-wide alignment
Key Management Risks
Users are responsible for:
-
Managing private keys
-
Securing their devices
Loss of keys can lead to access issues.
Performance and Latency
Cryptographic verification must be:
-
Fast enough for high-throughput entry نقاط
-
Reliable in low-connectivity environments
Future Trends
Passkey-Based Authentication
Passkeys—based on public-key cryptography—are gaining adoption as a secure, user-friendly alternative to passwords and biometrics.
Privacy-Preserving Analytics
Event platforms will increasingly use:
-
Aggregated, anonymized data
-
Differential privacy techniques
-
Federated learning models
to derive insights without compromising identity.
Integration with Digital Identity Ecosystems
Event identity systems will connect with:
-
Government-issued digital IDs
-
Enterprise identity systems
-
Global identity networks
Regulatory-Driven Innovation
As privacy regulations evolve, they will:
-
Accelerate adoption of decentralized identity
-
Standardize compliance frameworks
-
Encourage privacy-by-design architectures
Conclusion: Trust as the New Authentication Layer
Biometric-free authentication represents a shift from convenience-driven identity systems to trust-driven architectures. By prioritizing privacy, decentralization, and user control, these systems address the growing concerns סביב data security and surveillance.
For event technology leaders, the adoption of privacy-first identity systems is both a strategic and operational decision. It enables secure, scalable, and compliant identity management while enhancing attendee trust and experience.
As digital events become more interconnected and data-intensive, identity will no longer be just a gateway—it will be a critical component of the overall event experience. Designing it with privacy at the core is no longer optional; it is foundational.
Related